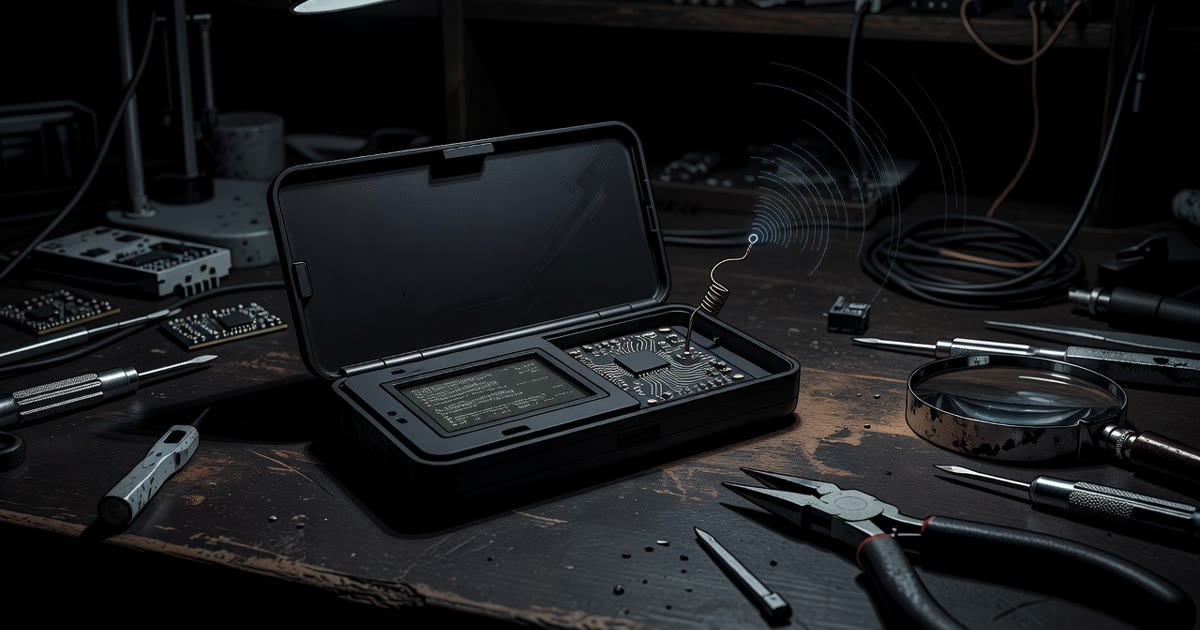
Ledger confirmed on 13 October 2026 that hardware wallets sold by Southeast Asian reseller CryptoBilis contained an unauthorized implant. The chip reads the 24-word recovery phrase off the screen during setup and sends it over LTE. Losses tied to the 9 October disclosure are estimated around 86 million dollars. Ledger has not confirmed a total.
What happened
Ledger Donjon examined an affected signer and found a separate board inside the enclosure. When the device displays the recovery phrase, a microcontroller decodes the words and transmits them using a provisioned eSIM. The Secure Element and Ledger OS were not modified. Transactions and signatures were not altered. This is a physical supply-chain attack, not a software breach of Ledger.
Every confirmed loss so far involves a device sold through CryptoBilis, which sold in Indonesia, Malaysia, and the Philippines. CryptoBilis has stopped selling hardware wallets. Trezor and OneKey have cut ties with the reseller. Independent teardowns, including one by Mark Karpeles, described an LTE module on the screen bus of a still-sealed Nano X.
Who is affected
Anyone who bought a Ledger signer from CryptoBilis, and anyone whose recovery phrase was displayed on a device from that channel. Ledger says it has not verified a drain from a device bought elsewhere. Reports of implants outside that channel are still being checked.
What to do now
- If a signer came from CryptoBilis, treat the seed as stolen and move funds to a new wallet bought from Ledger or another trusted channel.
- Do not type the old recovery phrase into a replacement device until the funds have been moved.
- Buy hardware wallets only from the manufacturer or a distributor you can verify. A sealed box is not proof the board inside is genuine.
Source: SecurityWeek, 13 October 2026.
Also on the blog
- GitLab CVE-2026-97229: CVSS 10 unauthenticated RCE
- Danfoss fridge controllers hijacked at 500 French stores
- NetScaler CVE-2026-107406: CVSS 9.5 SAML memory overflow
- Anthropic cuts live internet from all internal Claude evaluations
Next step: If this is on your network or a client's, ask Matthews Enterprises to check exposure.